ZTNA for PNG businesses gives employees, contractors and branch teams secure access to the applications they need without opening the wider business network. Sprint Networks has already put this into practice for Hornibrook NGI in Lae and Golden Manufacturers in Suva, so staff in the office, on site and on the road can reach their ERP safely.
A finance manager working away from the office needs to approve an invoice. A project engineer on a remote site needs to check stock in the ERP. An external IT contractor needs access to one application for maintenance.
Each person has a legitimate reason to connect. But how much of the business network should that connection open up?
For businesses in Papua New Guinea and across the Pacific with branch offices, project sites, travelling staff and cloud-hosted systems, controlling access is an important part of protecting everyday operations. That is where ZTNA for PNG businesses helps. Zero Trust Network Access, or ZTNA, gives people access to the applications they need while keeping other systems out of reach.
ZTNA for PNG businesses: what is Zero Trust Network Access?
ZTNA controls access to business applications using identity and access policies. Being connected to the office network, or knowing a password, should not automatically make someone trusted to reach everything. This follows the zero trust principle that access must be checked rather than assumed from a user’s location.
For example, an employee authorised to use the ERP can be given a connection to that application without also opening a route to unrelated servers. The ERP’s own permissions still decide what the employee can view or change once signed in. This approach follows the principles in NIST’s Zero Trust Architecture guidance.
How does ZTNA for PNG businesses work?
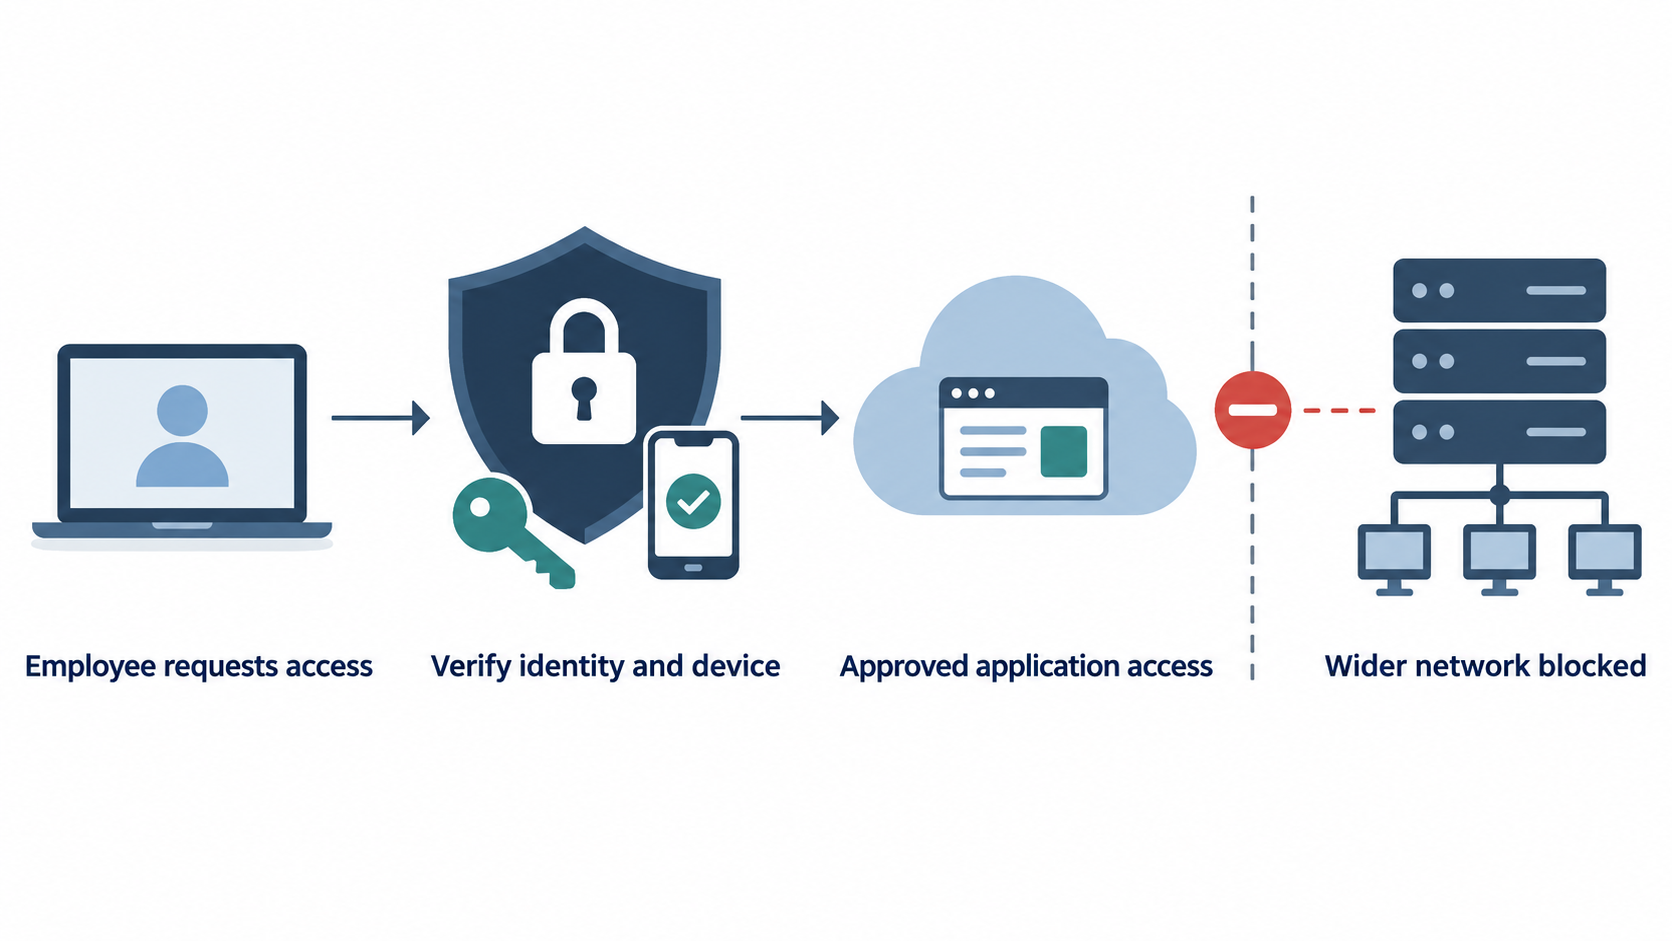
When someone requests access, a ZTNA service checks whether the connection meets the business’s rules. Depending on the solution, those checks can include the user’s identity, their assigned group, the application requested and the security condition of their device.
Multi-factor authentication strengthens the sign-in. Device checks help block computers that do not meet required security standards. Policies can also reassess access as conditions change. These capabilities must be set up around how the business actually works.
Consider a supplier maintaining a stock-management application. Their access can be limited to that application and removed when the work finishes. They do not need general connectivity to the company’s other systems.
4 access risks that ZTNA for PNG businesses reduces
The underlying risk is poorly controlled access. A business without ZTNA is not automatically insecure, but it needs effective controls that address the same problems:
- Stolen credentials can provide a wider foothold. If a compromised account can reach many systems, an attacker has more opportunities to explore the network.
- An infected device can put other systems at risk. Broad connectivity may help an attacker move from the original device towards other resources.
- Contractors can keep access they no longer need. Permissions that remain after a project ends create avoidable exposure.
- Staff can build up permissions over time. Role changes and temporary responsibilities can leave access rights behind unless someone reviews them.
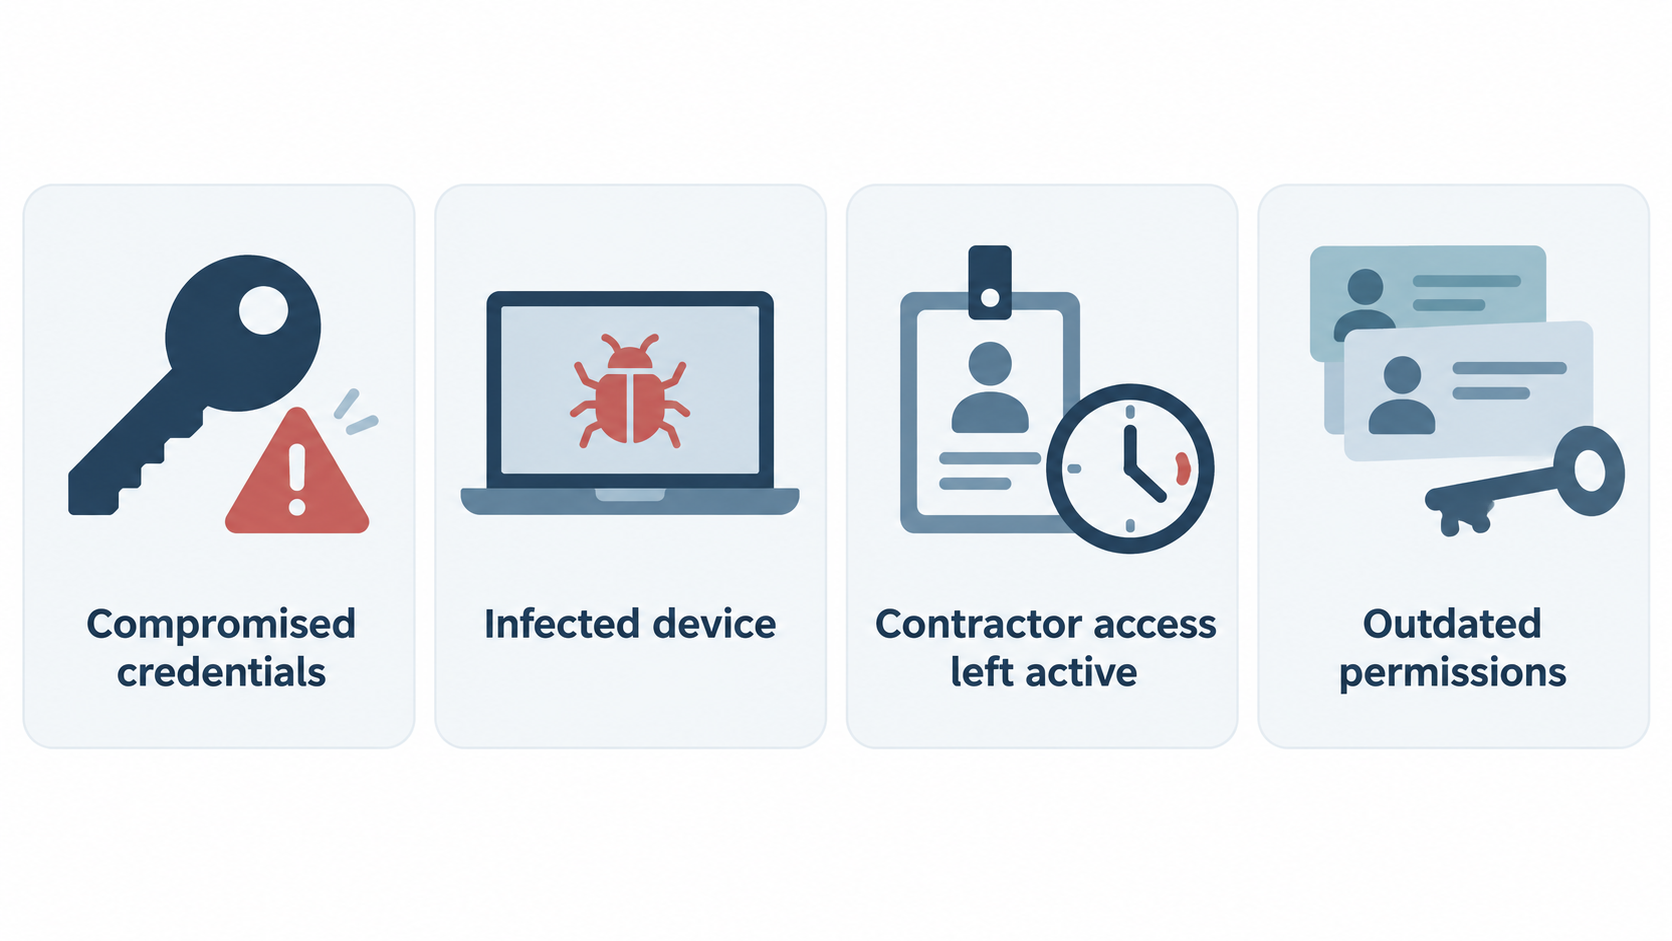
Limiting each connection to the resources needed for the task reduces these opportunities. Protecting resources individually and giving minimum necessary access are central goals of zero trust.
ZTNA in practice: two Pacific businesses, two real results
Theory is useful, but Pacific businesses want to know it works on their own connections and sites. Here is how Sprint Networks has delivered ZTNA for PNG businesses and Pacific organisations, using two clients with very different starting points.
Hornibrook NGI, Lae PNG: from password-only remote access to zero trust in one week
Hornibrook NGI is a construction and civil engineering business with its head office in Lae and teams working on projects across Papua New Guinea. Staff rely on the ERP for projects, purchasing, stock, payroll and finance, from the office, from site and on the road.
In early 2026 Hornibrook spotted suspicious activity on its network. Its remote access was open to the internet and protected by a password alone, so one guessed or stolen password could open the door to the whole business.
Sprint Networks engineers flew to Lae in March 2026 and completed the work in seven days, from first audit to go-live. Remote access is now built on zero trust:
- Staff sign in with multi-factor authentication, so a stolen password on its own is not enough.
- A small security client on each laptop applies the same checks on site, at home or on the road.
- Users reach only approved applications such as the ERP, never the whole office network.
- ERP traffic is given priority, so the system stays responsive on limited PNG internet links.
The outcome: no security incidents in the six months since go-live, with Sprint Networks monitoring the environment 24/7. Zero trust access was paired with a next-generation firewall and separate secure zones inside the network, so if one device is ever compromised the problem stays contained.
Read the full Hornibrook NGI case study.
Golden Manufacturers, Suva Fiji: secure remote access to a cloud ERP
Golden Manufacturers Limited (GML) makes cartons, packaging and labels for some of Fiji’s best-known products. Orders, stock, production and deliveries run through Microsoft Dynamics 365 Business Central, hosted in Azure. GML needed a dependable route to that ERP and a secure way for staff to reach it while away from the office.
As part of a wider SD-WAN project completed in January 2026, Sprint Networks introduced ZTNA for authorised remote employees. They now reach Business Central at the application level, without first being given broad access to the office network.
The outcome: secure remote ERP access, plus two working internet paths from Suva head office to Azure with automatic failover that was tested before handover, and ERP traffic given priority over general internet use.
Read the full Golden Manufacturers case study.
Hornibrook and GML at a glance
| Hornibrook NGI | Golden Manufacturers (GML) | |
|---|---|---|
| Location | Lae, PNG, plus project sites | Suva, Fiji, plus branches |
| Industry | Construction and civil engineering | Packaging manufacturing |
| Starting point | Remote access open to the internet, password only | Staff needed secure remote access to a cloud ERP |
| How ZTNA was used | Multi-factor sign-in and access to approved apps only, on any connection | Application-level access to Business Central in Azure |
| Paired with | Next-generation firewall, secure zones, 24/7 monitoring | SD-WAN with tested failover and ERP priority |
| Result | Live in 7 days, 0 incidents in 6 months | Secure remote ERP access, completed January 2026 |
What both projects teach about ZTNA for PNG businesses
ZTNA works best as part of a wider design. At Hornibrook it sits alongside a firewall and secure zones. At GML it sits alongside SD-WAN. ZTNA controls who reaches which application; it does not fix an unreliable link or remove every threat on an authorised device.
Start with how people actually work. A good rollout begins by listing the applications people need, who should use them and which devices they connect from. Policies are then tested with real staff workflows before going wider.
Plan for Pacific internet conditions. Links in PNG and the islands can be limited. Giving the ERP priority means security checks do not come at the cost of a slow system.
Someone has to keep watching. Permissions need reviewing, departing users need removing and unusual access attempts need investigating. That is why both clients’ networks are managed by a team rather than left to run on their own.
Is your business in the same position?
If you are considering ZTNA for PNG businesses like yours, it is worth a conversation when any of these sound familiar:
- Staff reach your ERP or files from home, project sites or while travelling.
- Remote access relies on a username and password alone.
- Contractors or suppliers have access that was never removed.
- Every device in the office sits on the same network.
Sprint Networks delivers ZTNA for PNG businesses and Pacific organisations as part of our Secure ERP Access and SASE services, backed by managed cybersecurity and 24/7 monitoring. Book a free security check and a senior engineer will show you where your access gaps are, or contact Sprint Networks to talk through your requirements. You can also browse all our client case studies.
Frequently asked questions
What is ZTNA, and how does it protect business applications?
ZTNA gives authorised users access to specific applications according to access policies. It limits unnecessary access to other systems, reducing the reach of a compromised account or device.
Is ZTNA the same as secure ERP access?
No. Secure ERP access is the goal; ZTNA is one technology that helps achieve it. ERP permissions, multi-factor authentication and device security also play a part.
Can employees use ZTNA when working remotely or on project sites?
Yes. ZTNA lets authorised employees connect to approved applications from outside the office, provided they have connectivity and meet the access requirements. At Hornibrook NGI, the same checks apply whether staff are in Lae, on a project site or travelling.
Does ZTNA for PNG businesses work on slower internet links?
Yes, but it should be designed for those conditions. In both the Hornibrook and GML projects, ERP traffic was given priority so the system stays responsive while every connection is still checked.
How did Sprint Networks use ZTNA for Hornibrook NGI?
Sprint Networks replaced password-only remote access with zero trust access using multi-factor sign-in, so staff reach only approved applications such as the ERP. The project went from audit to go-live in seven days, with no security incidents in the six months since.
How did Sprint Networks use ZTNA for GML?
Sprint Networks gave authorised GML employees remote access to their Business Central ERP in Azure through ZTNA, without first granting broad access to the wider office network.
3 Responses